
Forwarded from 卩ro 爪Cracker
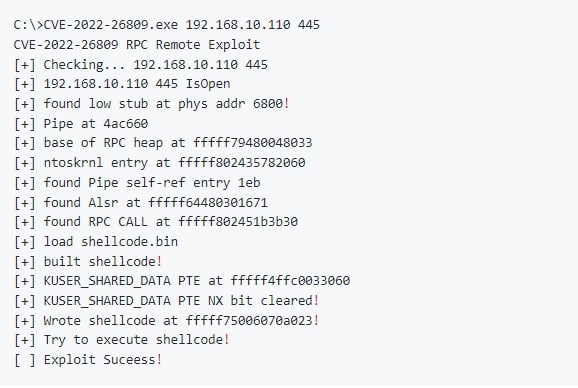
CVE-2022-26809 RCE Exploit
Weakness in a core Windows component (RPC) earned a CVSS score of 9.8 not without a reason, as the attack does not require authentication and can be executed remotely over a network, and can result in remote code execution (RCE) with the privileges of the RPC service, which depends on the process hosting the RPC runtime.
That critcal bug, with a bit of luck, allows to gain access to unpatched Windows host running SMB. The vulnerability can be exploited both from outside the network in order to breach it as well as between machines in the network.
https://github.com/rkxxz/CVE-2022-26809
Vendor Information:
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2022-26809
https://www.pwndefend.com/2022/04/14/cve-2022-26809/
#cve #poc #exploit
Forwarded from 卩ro 爪Cracker
CVE-2022-30190 Follina POC
Host exploit.html on localhost, port 80. Open the docx to pop calc.
To change the remote address the doc points to, open in 7Z and edit word\rels\document.xml.rels to point to a new location. YOU MUST keep the exclamation mark. It will literally not run if you omit this from the end of the URL.
The exploit must contain at least 3541 characters before the window.location.href, and they must be within the script tag. There is about 6000 or so included in the exploit.html
https://github.com/onecloudemoji/CVE-2022-30190
#cve #poc
Forwarded from Bhartiya Hunters🇮🇳 (Founder & CEO •)
Forwarded from Bhartiya Hunters🇮🇳 (Founder & CEO •)
Bug bounty Hunting 🔥💫🇮🇳
#BBH #Pentesting #RedTeam #EthicalHacking #BugBounty #Vulnerabilities
Shared by @Indianshunters
https://youtu.be/YKE3kzbwRUo
#BBH #Pentesting #RedTeam #EthicalHacking #BugBounty #Vulnerabilities
Shared by @Indianshunters
https://youtu.be/YKE3kzbwRUo
👍4
CVE-2022-42889 PoC
This is Proof of Concept for the vulnerability CVE-2022-42889. This code will run the JavaScript code 195 + 324. If vulnerable the output should be:
Details:
https://blogs.apache.org/security/entry/cve-2022-42889
#cve #poc
This is Proof of Concept for the vulnerability CVE-2022-42889. This code will run the JavaScript code 195 + 324. If vulnerable the output should be:
PoC Output: 519
https://github.com/SeanWrightSec/CVE-2022-42889-PoCDetails:
https://blogs.apache.org/security/entry/cve-2022-42889
#cve #poc
GitHub
GitHub - SeanWrightSec/CVE-2022-42889-PoC: Proof of Concept for the Apache commons-text vulnerability CVE-2022-42889.
Proof of Concept for the Apache commons-text vulnerability CVE-2022-42889. - SeanWrightSec/CVE-2022-42889-PoC
#Threat_Research
1. Compromised PyTorch-nightly dependency chain between December 25th and December 30th, 2022
https://pytorch.org/blog/compromised-nightly-dependency
2. Google Home Vulnerability: Eavesdropping on Conversations
https://downrightnifty.me/blog/2022/12/26/hacking-google-home.html#poc-1-spy-on-victim
1. Compromised PyTorch-nightly dependency chain between December 25th and December 30th, 2022
https://pytorch.org/blog/compromised-nightly-dependency
2. Google Home Vulnerability: Eavesdropping on Conversations
https://downrightnifty.me/blog/2022/12/26/hacking-google-home.html#poc-1-spy-on-victim
Forwarded from CYBER TRICKS ZONE 🇮🇳🚩 (𝙋𝙧𝙤𝙩𝙤𝙘𝙤𝙡 𝙉𝙞𝙘𝙠)
Microsoft Exchange: OWASSRF + TabShell
(CVE-*2022-41076)*
The TabShell vulnerability its a form of Privilege Escalation which allows breaking out of the restricted Powershell Sandbox after you have successfully gained access through OWASSRF.
For a detailed write see research:
https://blog.viettelcybersecurity.com/tabshell-owassrf/
*PoC:
*
https://gist.github.com/testanull/518871a2e2057caa2bc9c6ae6634103e
#owa #ssrf #tabshell #poc
@virus303
@NetEditors
👍2